

February 23, 2013
LulzSec Hacker Sabu’s Sentencing Postponed
 The sentencing of Hector Xavier Monsegur – better known as Sabu, the leader of the infamous LulzSec hacker collective – has been postponed once again without any explanation.
According to The Guardian, Monsegur was scheduled to appear at a Manhattan federal court on Friday where he should have been sentenced for 10 counts of hacking, one count of identity theft and one count of bank fraud.
This is not the first time when the hacker’s sentencing is postponed. Back in August, 2012, authorities requested a six-month adjournment because Sabu was still cooperating with the government.
Cooperation with the government is what made Monsegur become the symbol of treason among hacktivists. In March 2012, the alleged members of the LulzSec group were arrested after being ratted out by Sabu.
He was first arrested in June 2011, but the FBI released him in exchange for his assistance in apprehending other hackers.
Categories:
LulzSec Hackers,
Lulzsec Leader,
Sabu
June 16, 2011
LulzSec hackers claim breach of CIA website

CIA
Following their recent exploits with the U.S. Senate website, LulzSec has now made the CIA their target via a packet-flooding attack. While it’s highly unlikely that the CIA’s Website has any sensitive data residing on it, the notion of such a high profile target being attacked is bad enough. To be fair, packet-flooding simply means they crashed the CIA’s server, but it can be a rather problematic issue to network health if certain precautions aren’t taken. The key takeaway here is the target of the attack. Per LulzSec’s Twitter feed:

LulzSec Target CIA
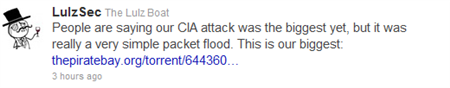
LulzSec says they packet-flooded the CIA
In the second tweet, their proclamation of their most severe exploit at this point is the release of internal information from Bethesda Software. The release included server admin configurations, admin staff and blog user hashes, server logs, and mappings of Arkane, Bethblog, Brink codes, Brink signups, IDSoftware, Rage, and more.
While far more data was released with the Bethesda attack, the reason the CIA attack is considered their biggest is because of who it is, thus the potential repercussions.
Emails and Passwords
The last LulzSec-released list of email addresses and passwords totaled 26,000, and they were all obtained via hacked pornographic sites. This time, they’re keeping quiet about the sources of this latest list of culminated addresses. Regardless of the sources, here are 62,000+ email addresses and passwords just released. From their Twitter feed:

LulzSec releases 62,000 emails/passwords
Many users have taken to Twitter to let LulzSec know either how they have been attacked due to the leaked list, or how they have benefited by exploiting the leaked information. Make no mistake, LulzSec is essentially releasing this information into the hands of people with malicious intentions.
As with before, it is highly advised that you download the list and check for your email address so as to change your password. You can obtain the leaked list here (visit the link to download the file). Use the “find/search” functionality of your browser/text viewer to search for your email address once you download the 2.25 MB text file.
While neither of these latest activities were posted to LulzSec’s blog as official releases, it’s clear that they intend on utilizing any and every avenue they can to show off their exploits.
Lastly, while the image of a small group of individuals comes to mind in regards to the make-up of LulzSec, there is increasing speculation that the group — along with the equally-notorious rogue hacker group, Anonymous — is actually comprised of many people; possibly thousands. If true, this makes the efforts of these groups much more difficult to stop. However, as entities like the CIA and the U.S. Senate are targets of these groups, we may all soon find out just what the make of these groups really is.
How do you feel about LulzSec’s latest actions? Share your thoughts in the comments below!
Categories:
CIA,
Hacking,
LulSec,
Lulz Security,
LulzSec Hackers,
Tech News
Subscribe to:
Posts (Atom)